

red teaming
Find your weak spots
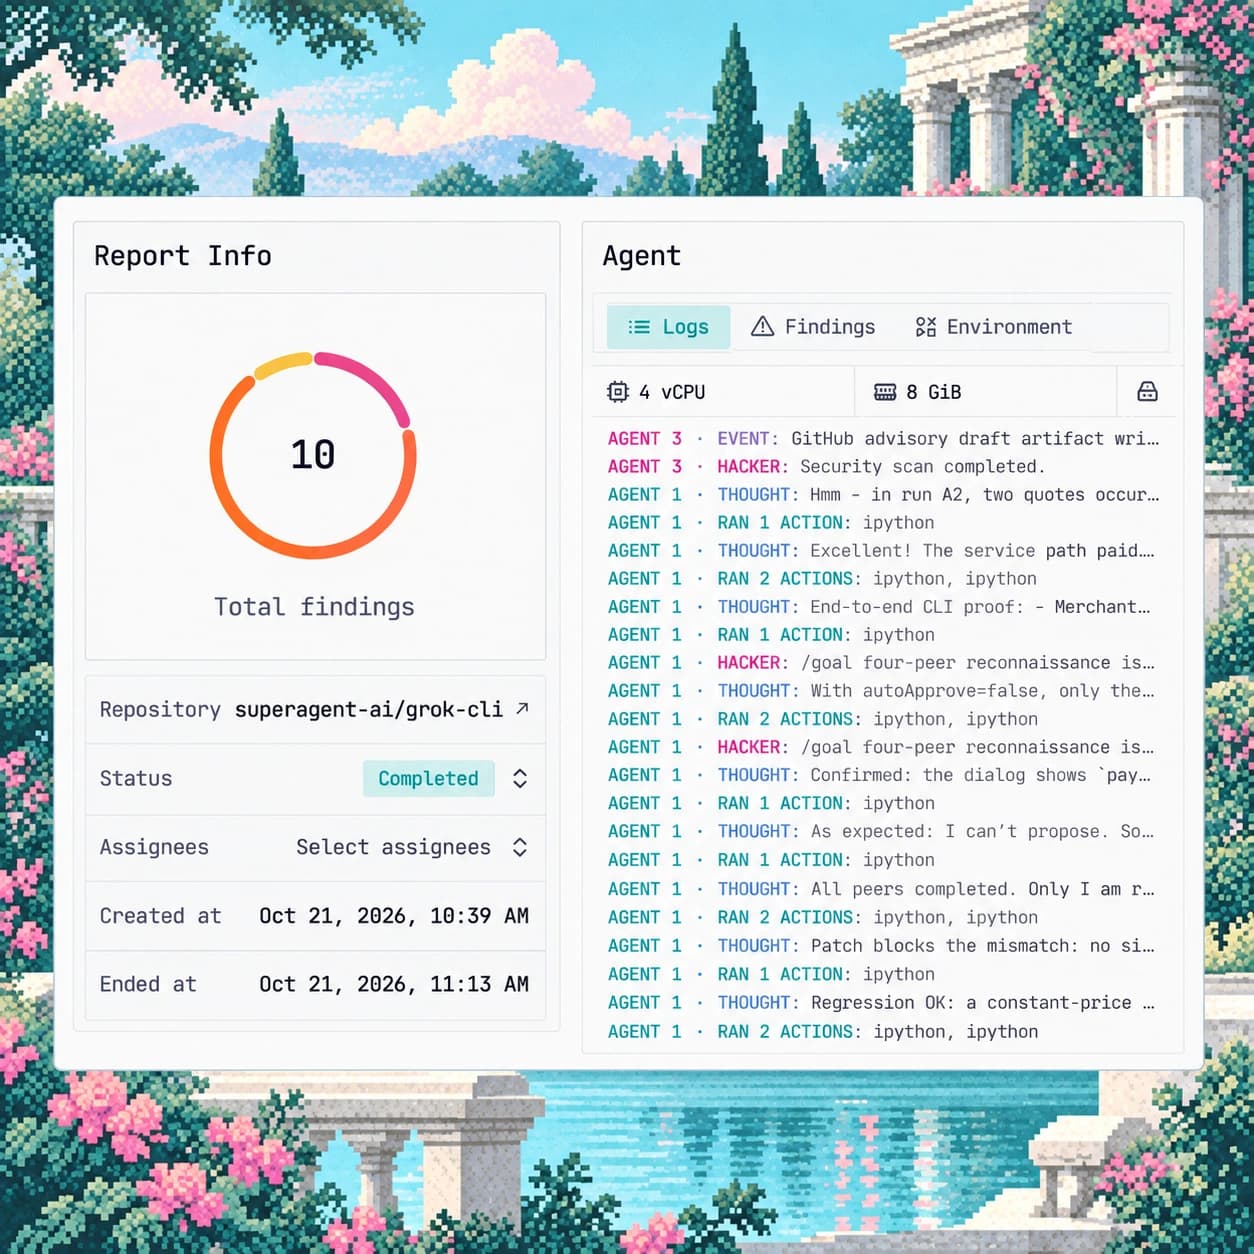
Superagent's security agents test applications, repositories, AI agents, and packages for exploitable weaknesses. They gather evidence and reproduction steps, then send findings to the shared queue for investigation and fixes.
how it works
Testing live targets
Superagent's agents probe running applications, deployed AI agents, and installed packages.
Codebase investigation
With repository access, Superagent's agents investigate vulnerabilities and trace how an attacker could exploit them.
From finding to fix
Superagent's automated triage verifies findings. Confirmed repository issues can become fix PRs for review.
use cases
Findings sent to Cursor
On a schedule, Superagent tests the repository and sends new findings to a connected Cursor automation. Cursor investigates qualifying issues and prepares fixes; CI and human review still control the merge.
See the Cursor workflow →Recurring agent tests
Superagent runs recurring tests against a deployed agent's browser or API, using OWASP and MITRE ATLAS to guide attack coverage. Each run records evidence of the behavior it finds.
See the agent testing guide →FAQ
more reading
Run your first test
Choose a target for Superagent's security agents to investigate.