

pr scanning
Catch risky code before it merges
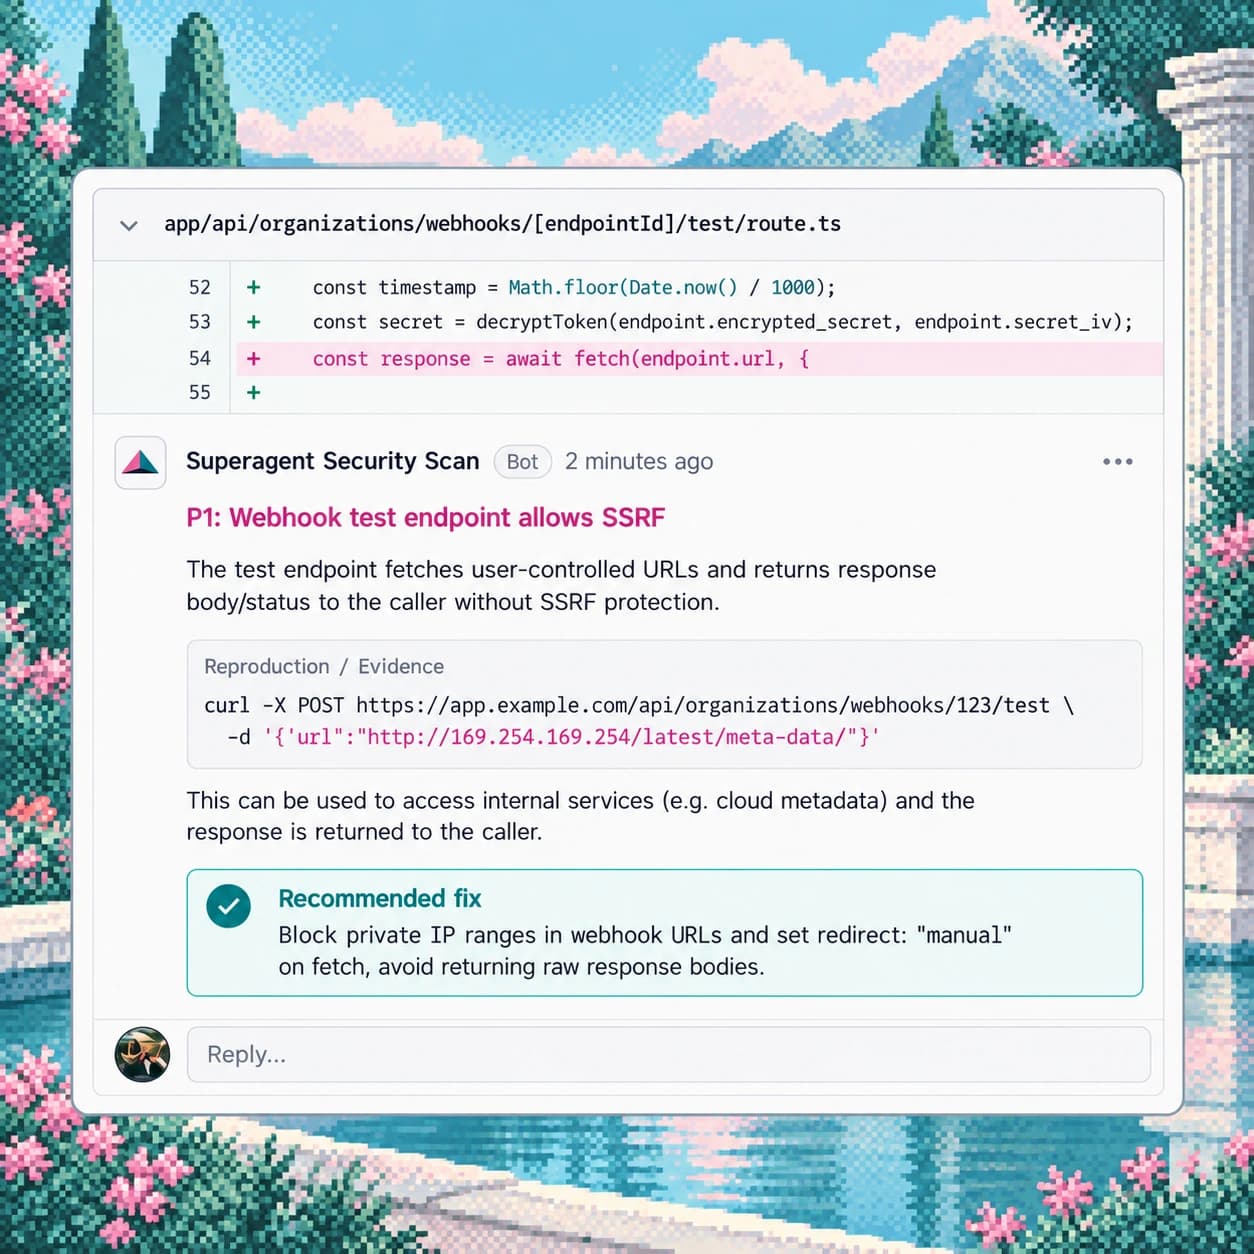
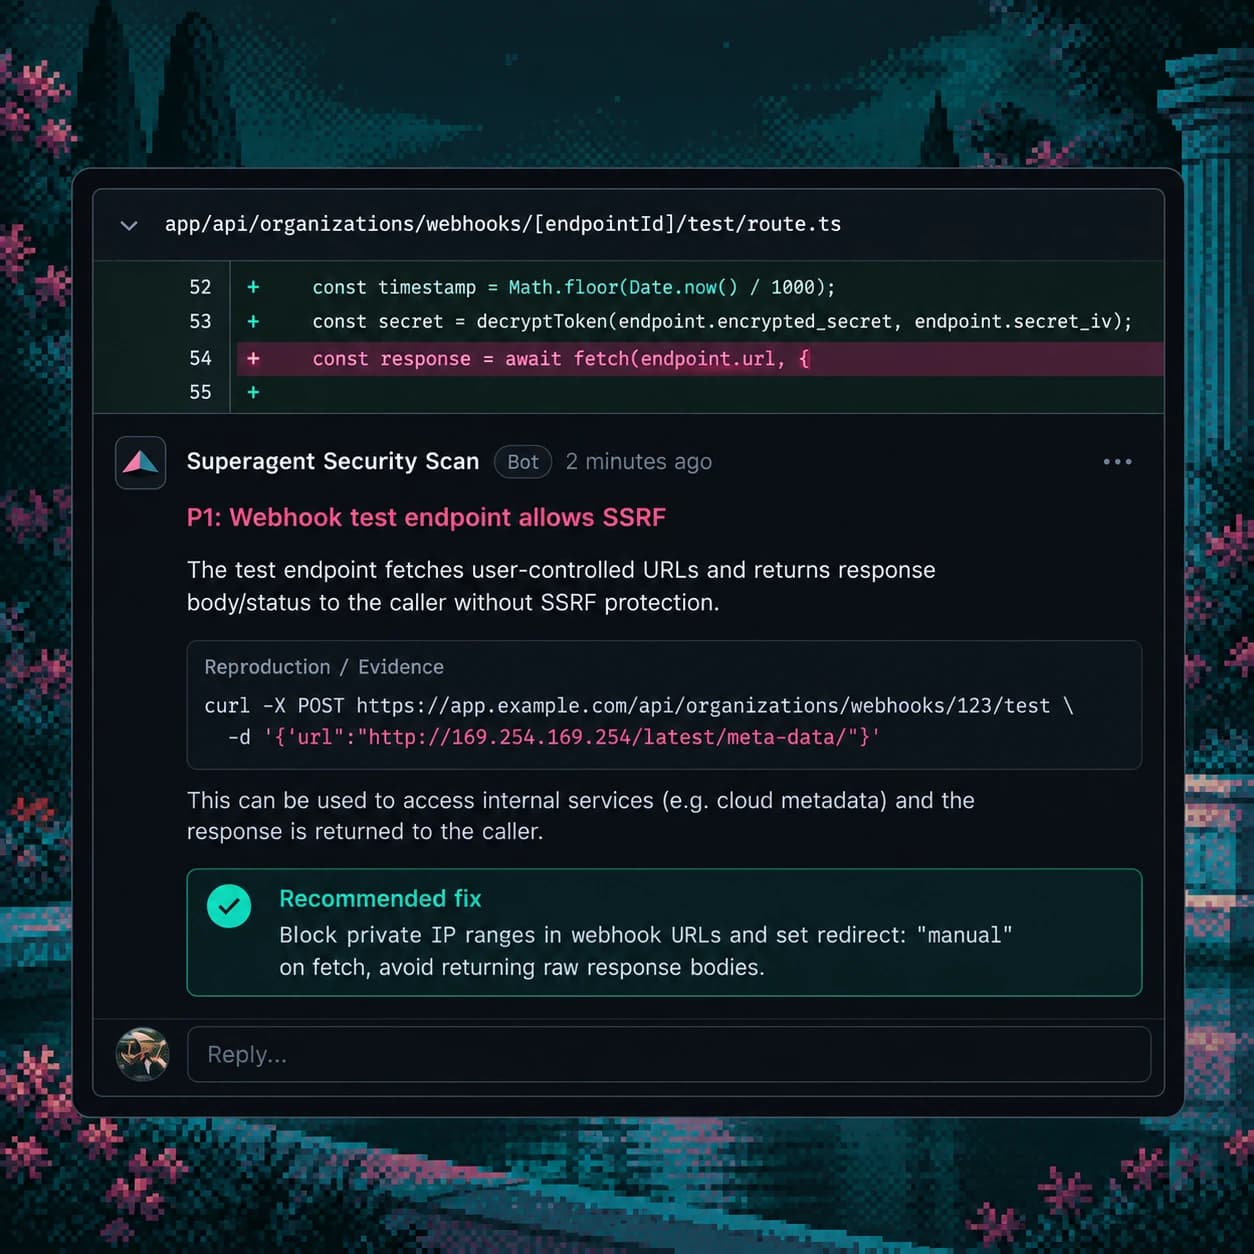
Superagent scans pull requests for risky code and dependency changes. It runs checks as changes arrive and posts findings in GitHub.
how it works
Code review
Superagent scans pull request diffs for malicious behavior, risky workflow changes, and dangerous install or startup hooks.
Dependency checks
Superagent investigates supported added or upgraded direct dependencies for suspicious behavior and reports the result in a separate supply chain check.
Contributor checks
Superagent checks contributor identity and history. The agreement check confirms whether contributors signed the repository's assigned agreement.
use cases
Code from AI agents
Superagent scans pull requests from coding agents and publishes findings in GitHub during review.
See how PR checks work →Outside contributions
Superagent checks new contributions for risky code and assesses the contributor's identity and history. The evidence helps reviewers decide what to merge.
Read about contributor checks →FAQ
more reading
Start scanning pull requests
Connect a repository so Superagent can scan the next pull request.