

runtime guardrails
Set limits for agents
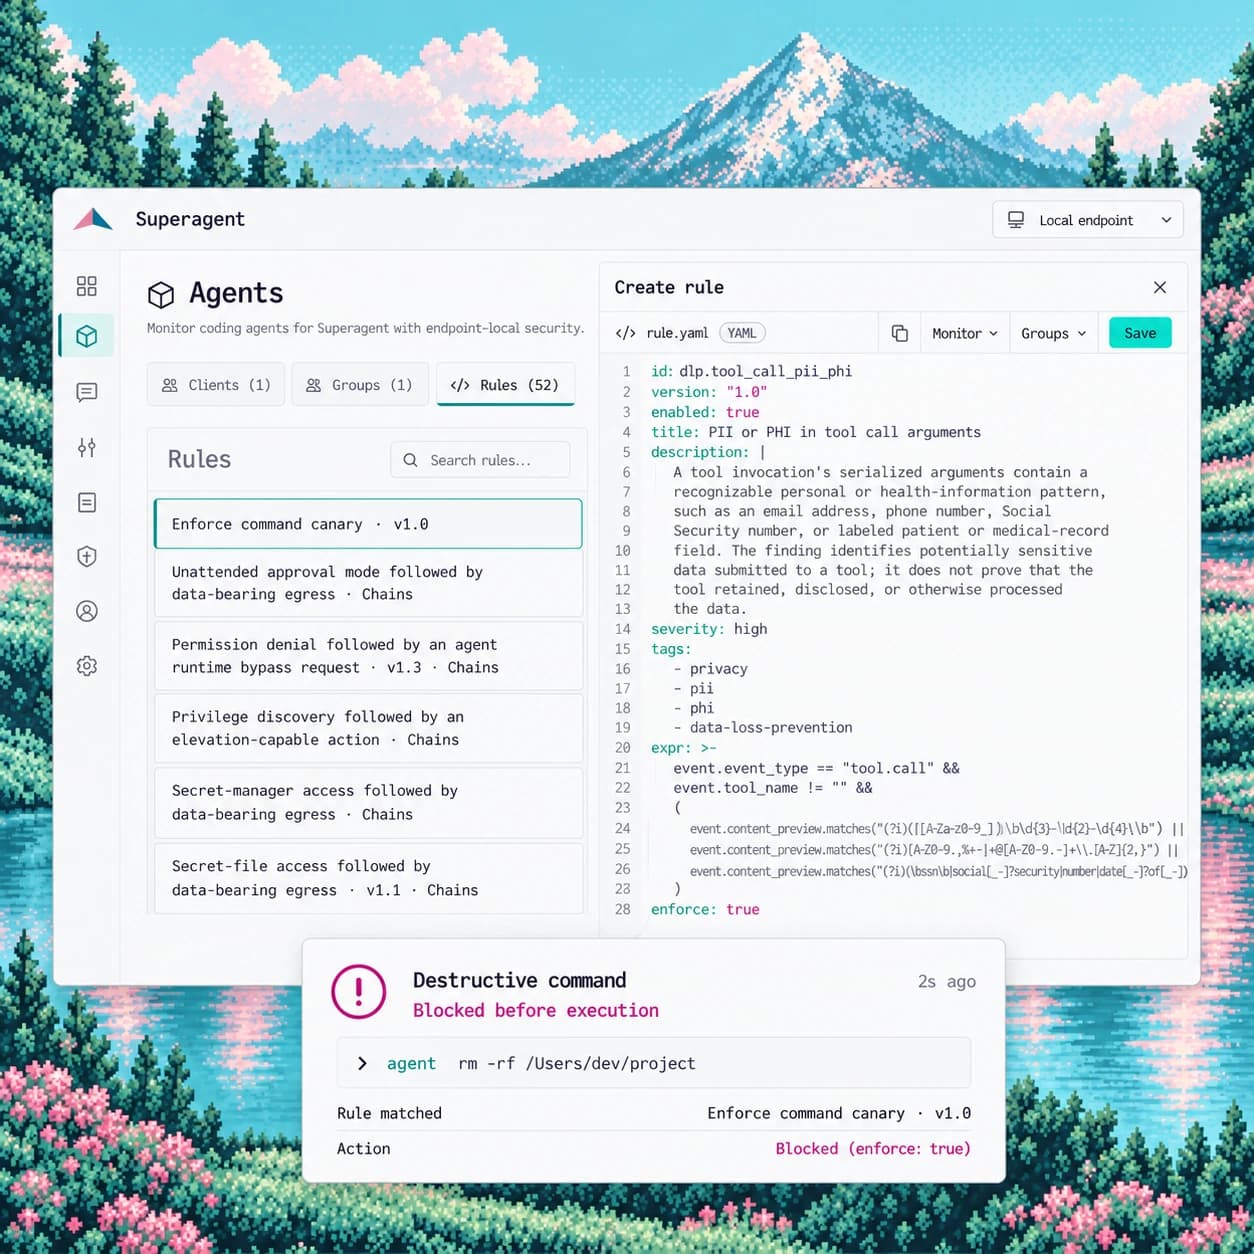
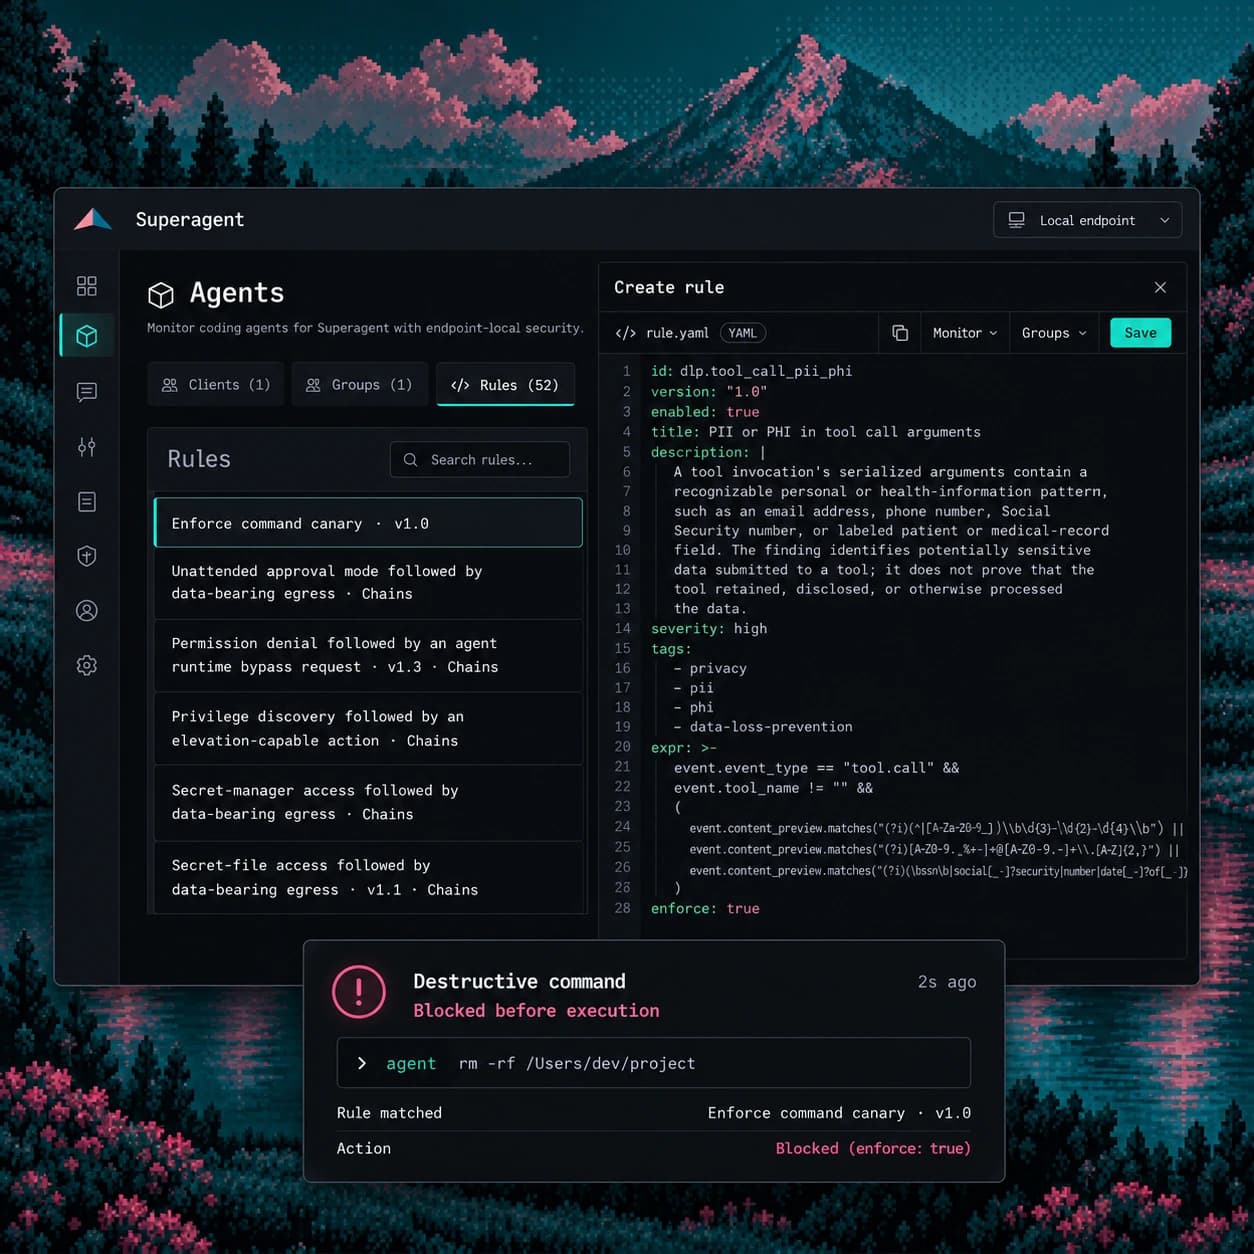
Superagent monitors agent activity on workstations and cloud hosts. It evaluates your rules locally, reports matches, and blocks supported actions when enforcement is enabled.
how it works
Local monitoring
Superagent evaluates command, file, and tool events against local security rules. Findings appear in Superagent and can reach your alert workflow.
Action blocking
Superagent blocks supported commands, file actions, or tool calls when they match an enforced rule.
Rules across hosts
Superagent distributes the rule catalog assigned to each client group. Each endpoint validates an update before activating it.
use cases
Sensitive arguments in Pi commands
Superagent evaluates the local rule and blocks supported Pi commands whose arguments match the personal or health data patterns. It sends redacted alerts to the monitoring workflow.
See the Pi rule example →Environment files on agent hosts
Superagent evaluates attempts to read environment files against your local rules. Supported hooks can block matching actions, and findings appear in Superagent.
Read about runtime rules →FAQ
more reading
Set up your first agent host
Pair a client so Superagent can apply local rules and report risky activity.