

dependency validation
Dependency validation
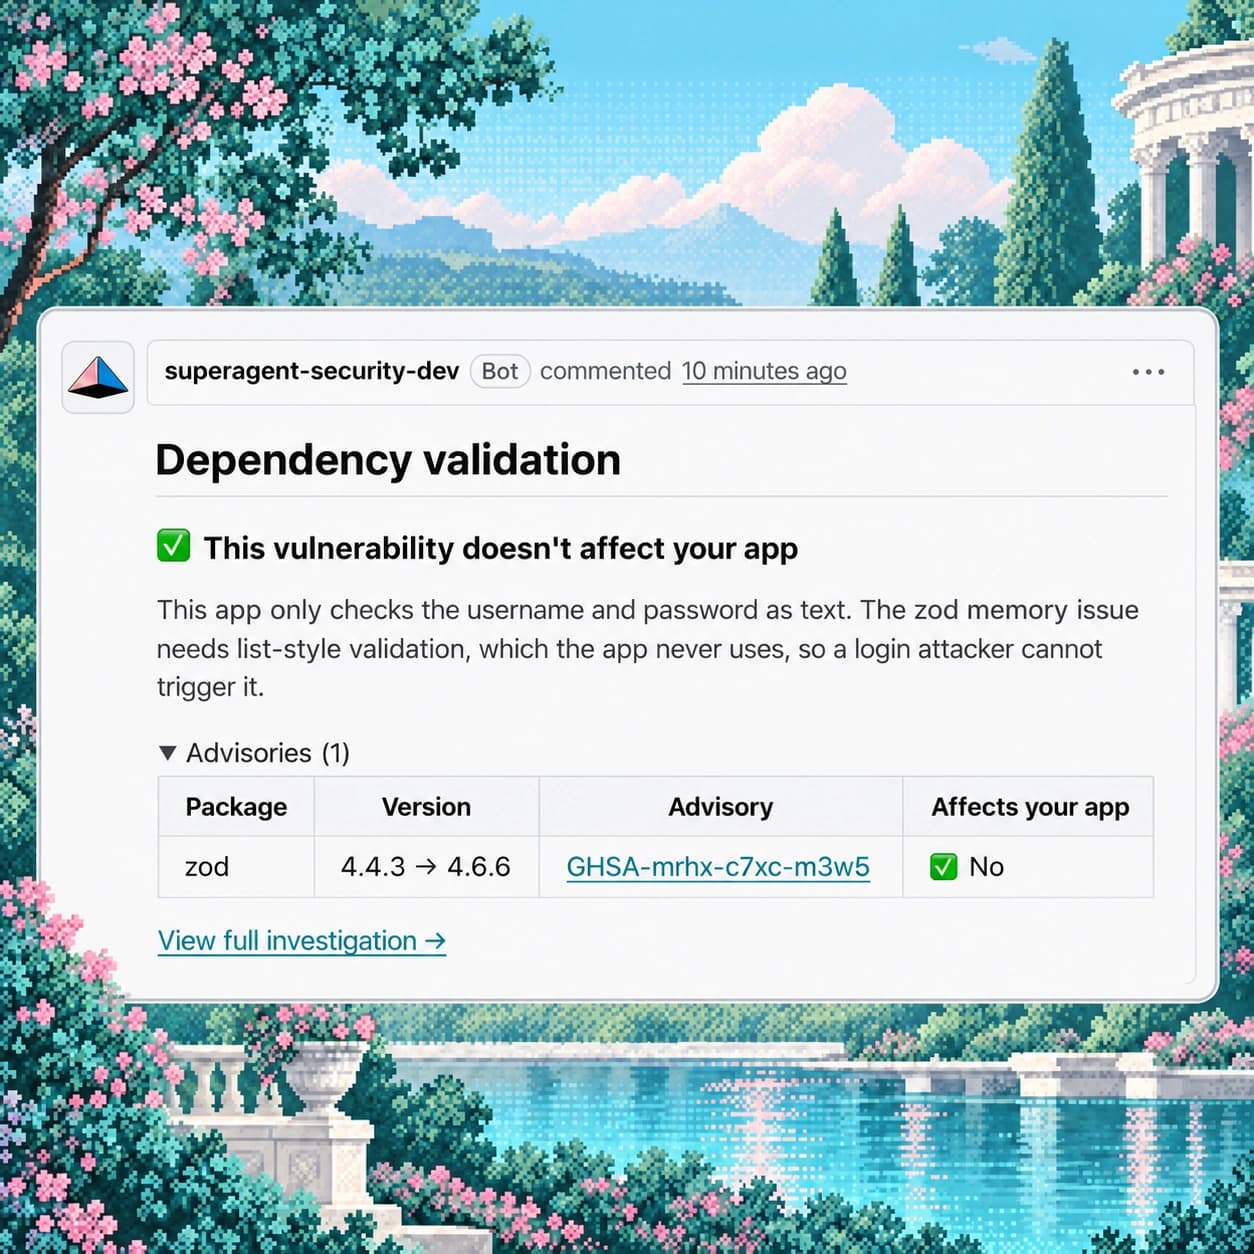
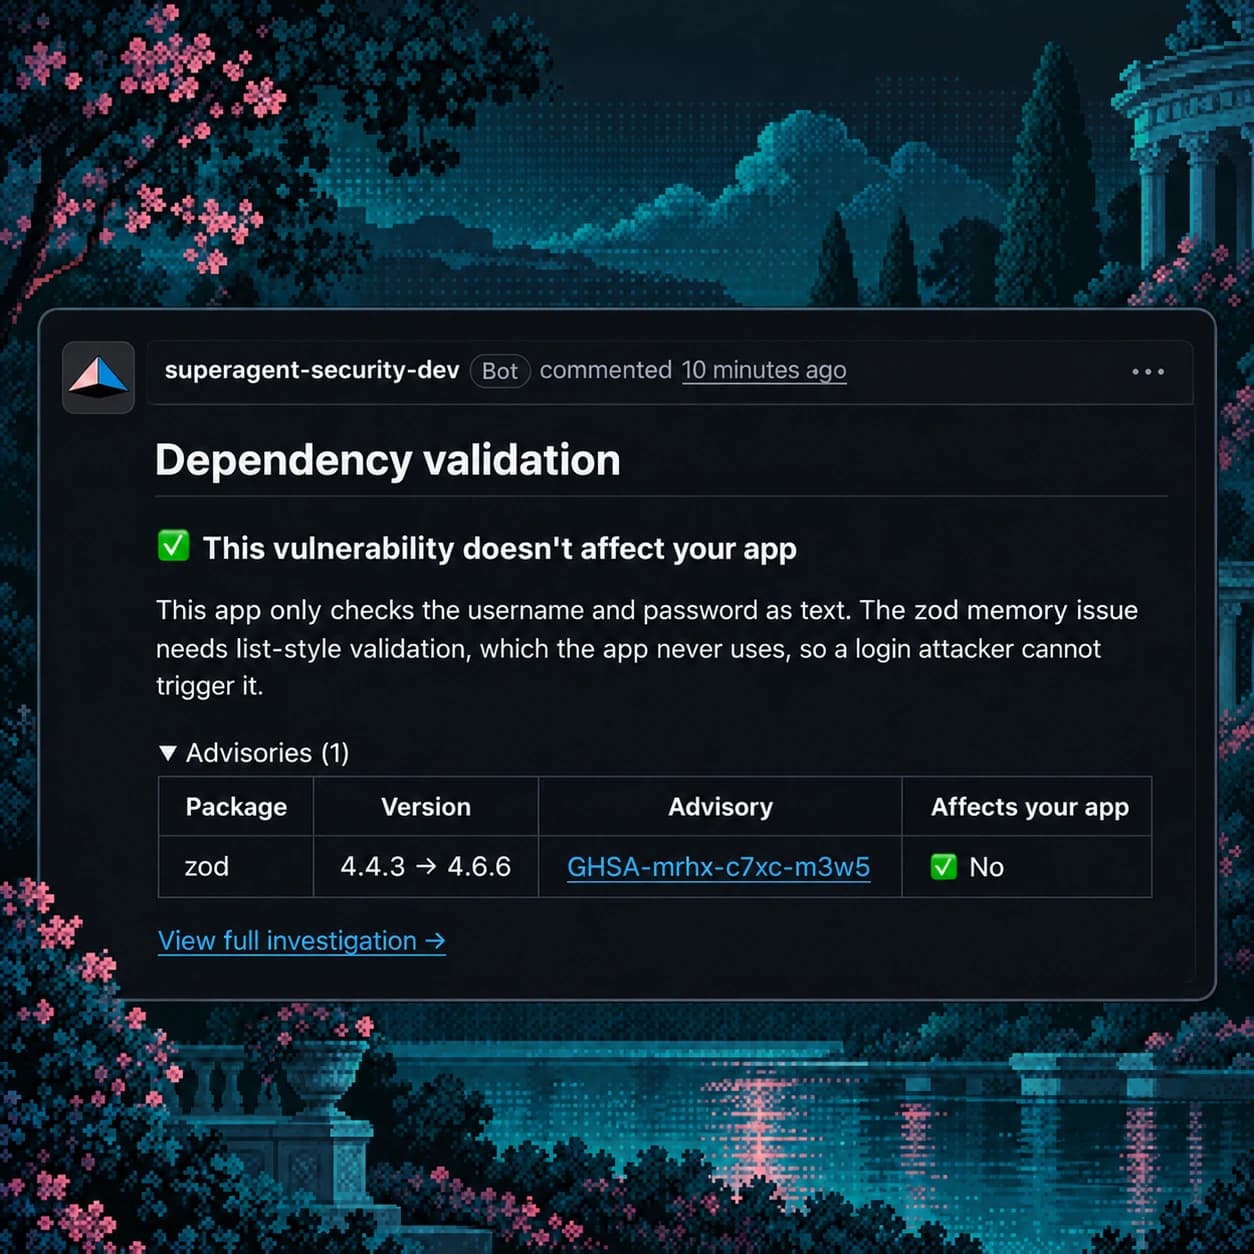
A vulnerable dependency does not always make your application exploitable. Superagent tests reported vulnerabilities in your app and verifies proposed fixes, so you can prioritize dependency updates with evidence.
how it works
Test application impact
Superagent runs your application in an isolated environment and attempts to exploit the reported dependency vulnerabilities to see which ones affect your app.
Validate the update
For confirmed vulnerabilities, Superagent repeats the attack with the dependency update installed. It checks that the attack fails and the application still works.
Prioritize with evidence
An independent agent verifies the evidence. Superagent reports application impact, fix status, and recommended priority on the pull request to help you decide what to merge.
use cases
Find the updates that matter
Use application testing to distinguish exploitable vulnerabilities from alerts that do not apply. Review verified fixes and identify vulnerabilities that still need attention.
See how validation works →Application tests with Devin
Superagent tests dependency vulnerabilities and verifies fixes. Your Devin automation runs application integration checks on the same update PR, giving reviewers both sets of results.
See the Devin workflow →FAQ
more reading
Prioritize your dependency updates
Connect a repository and enable Dependency Validation for Dependabot and Renovate security pull requests.